
A probe into hacked supermarket refrigeration systems in France shows how vulnerable legacy equipment can cause physical damage, while a Nigerian appeals court draws limits on cybercrime laws used against speech.
A cyberattack on supermarket refrigeration systems in France turned a vulnerability in aging equipment into a potential threat to food supplies, property and public safety. Authorities are investigating, but have not publicly identified a perpetrator or motive.
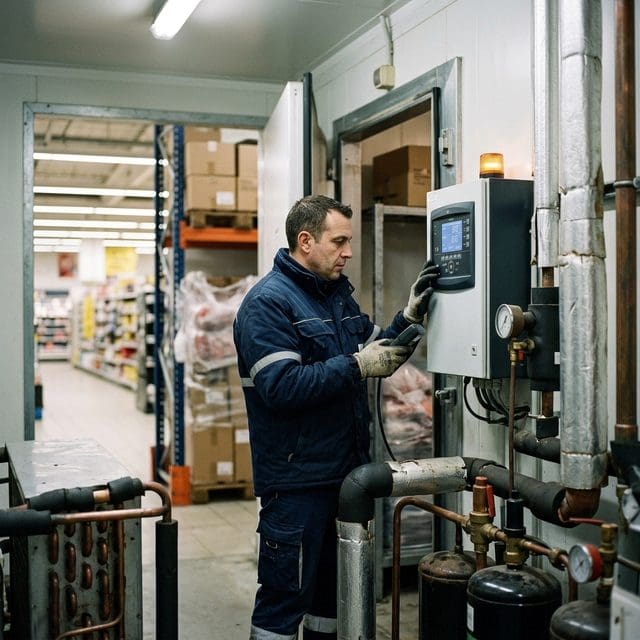
The Paris prosecutor opened an investigation into what it called a “large-scale” attack, AFP reported Oct. 12. Prosecutors are seeking to identify victims and determine whether the intrusion caused food losses or fires. Retailers told AFP that at least 300 Intermarché or Netto shops and more than 100 Coopérative U outlets were targeted, along with several E.Leclerc stores. The reported scope makes the incident more than a single-site equipment failure, though investigators have yet to publicly describe the full extent of damage.
Le Monde reported that hackers extended defrost cycles from one hour to eight, delaying alarms. One Intermarché operator said a cold room reached 50°C; a store in La Haye reported equipment temperatures reaching 80°C. The accounts show how an intrusion into operational technology can move beyond data theft or service disruption and affect the physical environment. A refrigeration controller may not be as visible as a payment network, but interference with its settings can put perishable goods and equipment at risk.
France’s national cybersecurity agency identified a vulnerability in software supplied by Danish manufacturer Danfoss and contacted the company. The agency is coordinating with European counterparts because other countries may also be affected, AFP reported. Danfoss said most affected equipment was legacy hardware that no longer receives software or security updates. AFP identified the AK-SM800 and AK-SC355 regulator systems, including an outdated-firmware version of the AK-SM800, as affected.
The available reporting does not establish who carried out the attack. There is no claim of responsibility, and a vulnerability in equipment used across borders does not prove a state-sponsored operation. That distinction matters: investigators must separate evidence of access and impact from attribution, particularly when an incident involving commercial infrastructure could invite geopolitical speculation. The prosecutor’s inquiry into victims, losses and fires will help establish the incident’s consequences, but the supplied reporting does not yet offer a public account of how the systems were accessed.
The case also raises a practical question of digital sovereignty. Retailers depend on specialized systems made and maintained by vendors abroad, while older equipment can remain in service after security support ends. National authorities can investigate and coordinate across borders, but replacing every embedded controller is not immediate. Ownership, maintenance and security updates are as consequential as debates over data centers and cloud providers. When equipment is no longer patched, operators may face a difficult choice between continued use and costly replacement; the reports do not specify what steps the affected retailers are taking.
A separate ruling in Nigeria highlights the risk that laws designed to address digital abuse can be used to punish speech. The Court of Appeal in Ilorin dismissed the Kwara State Government’s criminal defamation and cyberbullying case against Bukola Saraki, PUNCH reported Oct. 13.
The appellate panel said prosecution evidence did not show that Saraki’s comments caused a breach of the peace. Witness dissatisfaction alone, it said, did not establish violence or a threat to public order. The court added that the Administration of Criminal Justice Act, the Kwara Penal Code and cybercrime or cyberbullying provisions cannot be used simply to prosecute statements officials find offensive or uncomfortable.
The Nigerian ruling is unrelated to the French attack, but both cases illustrate the demands of cyber policy: operational competence and legal restraint. Governments need the capacity to protect connected infrastructure from intrusions that damage goods or equipment. They also need limits that prevent cybersecurity laws from becoming a shortcut for suppressing political expression. In Ilorin, the court’s reasoning turned on the evidence presented and the distinction between speech that displeases witnesses and speech shown to threaten public order.
For France, investigators must establish the extent of the compromise, determine whether losses or fires resulted and identify affected systems. The cross-border warning is that equipment past its security-support life can leave vulnerabilities embedded in ordinary commerce. In Nigeria, the court’s decision draws a different boundary around state power, rejecting prosecution based solely on official discomfort with speech.
Ryan Mitchell serves as a Staff Writer for Just Right News, where he anchors the desk for Cyber, Technology Policy, and Digital Sovereignty. In an era where the digital landscape has become as much a battlefield as any physical territory, Ryan provides a critical conservative lens on the forces shaping the future of American innovation and national security. His work is defined by a commitment to the idea that American leadership in the digital age is not just a matter of economic success, but a necessity for the preservation of global liberty.
Born and raised in Austin, Texas, Ryan’s perspective is deeply rooted in the Lone Star State’s tradition of independence and skepticism of centralized authority. Growing up in a city that transformed from a quiet state capital into a global technology hub, he witnessed firsthand the disruptive power of the tech industry. This upbringing instilled in him a firm belief in free-market principles and the necessity of protecting individual liberties from both government overreach and corporate overstep. His Texan background serves as a foundational compass, guiding his reporting toward stories that emphasize national resilience and the preservation of constitutional values in an increasingly virtual world.
Now based in San Francisco, California, Ryan operates from the epicenter of the very industry he scrutinizes. Living and working in the heart of Silicon Valley allows him to provide “boots on the ground” reporting that few conservative journalists can match. He navigates the cultural and political complexities of the Bay Area to bring Just Right News readers an inside look at the boardrooms and coding labs where the next generation of digital policy is forged. For Ryan, being stationed in San Francisco is a strategic choice; it allows him to challenge the prevailing ideological monoculture of the tech elite from within their own backyard, ensuring that the concerns of middle America are represented in the conversation about our digital future.
His beat—Cyber, Technology Policy, and Digital Sovereignty—covers the high-stakes world of data privacy, artificial intelligence, and the infrastructure of the modern web. Ryan is particularly focused on the concept of digital sovereignty, arguing that for a nation to remain truly free, it must maintain control over its own technological destiny and critical infrastructure. He frequently explores how international regulations and domestic policies impact the ability of American firms to compete without sacrificing the privacy or security of their citizens.
Central to his current body of work is his featured series, “The New Cold War.” Through this project, Ryan examines the escalating technological rivalry between the United States and its global adversaries. He delves into the complexities of state-sponsored hacking, the global race for semiconductor dominance, and the ideological struggle to define the rules of the internet. Ryan views this competition not merely as a commercial race, but as a fundamental defense of Western values against authoritarian digital models. Through his rigorous reporting and principled analysis, Ryan Mitchell ensures that the readers of Just Right News stay informed about the invisible forces defining the 21st century, always advocating for a future where technology serves the cause of freedom.