

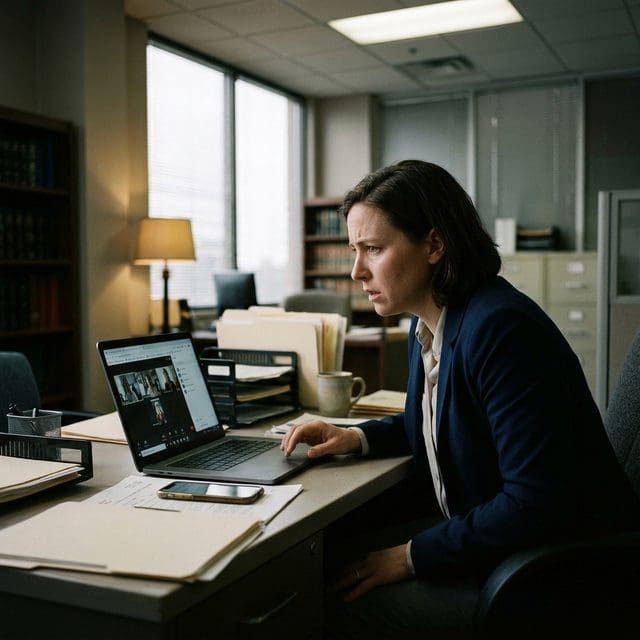
ReliaQuest says the extortion group is returning to law firms and using a Microsoft 365 Copilot access token to steal files without deploying malware.
Luna Moth is reportedly returning to law firms it previously tried to extort, this time with a social-engineering operation designed to turn an employee’s own access into a route to sensitive files. The group, also known as Silent Ransom Group, stole a second batch of data from apparent nonpayers in October and early November, according to cybersecurity firm ReliaQuest, which reported the campaign on Nov. 12.
ReliaQuest says firms targeted in May and August were among those approached again. Rather than rely on ransomware or a conspicuous malware infection, the latest tactic centers on impersonation: an attacker poses as IT support during a video call and persuades an employee to copy a Microsoft Graph access token from Microsoft 365 Copilot into a public text-sharing site.
The attackers then replay the token from their own infrastructure and can download thousands of files in about an hour, ReliaQuest said. The sequence may require only a blank-subject email containing a deliberately broken PDF, a spoofed call to an employee’s personal phone, a video meeting and the token handoff. The firm says the method does not require malware, remote-management software or a failed login.
That low-friction approach underscores a hard lesson for organizations: security controls can be undermined not only by software flaws, but by convincing an employee to perform an action that appears to be routine troubleshooting. In this case, the employee becomes the bridge between a legitimate work session and an attacker’s collection of corporate data.
Microsoft is the platform involved, not a reported perpetrator. ReliaQuest’s account describes criminals exploiting a stolen access token associated with Microsoft 365 Copilot; it does not say Microsoft’s systems were breached. Nor does the available reporting establish that Luna Moth is a state-sponsored actor. The campaign is presented as extortion-driven criminal activity, not a nation-state operation.
That distinction matters even as the incident belongs in a broader discussion of cyberspace as contested ground. Law firms hold confidential client material and can be attractive targets for criminals seeking leverage. A second theft from firms that apparently did not pay would increase pressure on victims and their clients, though ReliaQuest’s account does not identify the affected firms or describe the contents of the stolen files.
The episode also shows why a clean device and a successful login are not, by themselves, proof that an access request is safe. The reported chain does not depend on planting conventional malware or triggering an obvious authentication failure. Instead, the attacker seeks an already-issued credential through a staged conversation, then uses it to act from outside the victim’s organization.
ReliaQuest’s findings point to a practical challenge for defenders: suspicious activity may be scattered across email, phone calls, video meetings and cloud-file access. Reviewing those events in isolation can make each step look ordinary. The firm recommends correlating such records with Microsoft 365 activity and watching for unusual access patterns. It also recommends tighter controls over developer tools and unapproved screen-sharing software.
The wider stakes are not a new claim that every corporate breach is an act of geopolitical warfare. They are a reminder that digital access has become a strategic asset—and that adversaries, whether criminal or state-backed, may seek it through people as readily as through code. For organizations handling sensitive information, resisting that pressure requires clear procedures for verifying support requests and treating access tokens as credentials that must never be shared.
Ryan Mitchell serves as a Staff Writer for Just Right News, where he anchors the desk for Cyber, Technology Policy, and Digital Sovereignty. In an era where the digital landscape has become as much a battlefield as any physical territory, Ryan provides a critical conservative lens on the forces shaping the future of American innovation and national security. His work is defined by a commitment to the idea that American leadership in the digital age is not just a matter of economic success, but a necessity for the preservation of global liberty.
Born and raised in Austin, Texas, Ryan’s perspective is deeply rooted in the Lone Star State’s tradition of independence and skepticism of centralized authority. Growing up in a city that transformed from a quiet state capital into a global technology hub, he witnessed firsthand the disruptive power of the tech industry. This upbringing instilled in him a firm belief in free-market principles and the necessity of protecting individual liberties from both government overreach and corporate overstep. His Texan background serves as a foundational compass, guiding his reporting toward stories that emphasize national resilience and the preservation of constitutional values in an increasingly virtual world.
Now based in San Francisco, California, Ryan operates from the epicenter of the very industry he scrutinizes. Living and working in the heart of Silicon Valley allows him to provide “boots on the ground” reporting that few conservative journalists can match. He navigates the cultural and political complexities of the Bay Area to bring Just Right News readers an inside look at the boardrooms and coding labs where the next generation of digital policy is forged. For Ryan, being stationed in San Francisco is a strategic choice; it allows him to challenge the prevailing ideological monoculture of the tech elite from within their own backyard, ensuring that the concerns of middle America are represented in the conversation about our digital future.
His beat—Cyber, Technology Policy, and Digital Sovereignty—covers the high-stakes world of data privacy, artificial intelligence, and the infrastructure of the modern web. Ryan is particularly focused on the concept of digital sovereignty, arguing that for a nation to remain truly free, it must maintain control over its own technological destiny and critical infrastructure. He frequently explores how international regulations and domestic policies impact the ability of American firms to compete without sacrificing the privacy or security of their citizens.
Central to his current body of work is his featured series, “The New Cold War.” Through this project, Ryan examines the escalating technological rivalry between the United States and its global adversaries. He delves into the complexities of state-sponsored hacking, the global race for semiconductor dominance, and the ideological struggle to define the rules of the internet. Ryan views this competition not merely as a commercial race, but as a fundamental defense of Western values against authoritarian digital models. Through his rigorous reporting and principled analysis, Ryan Mitchell ensures that the readers of Just Right News stay informed about the invisible forces defining the 21st century, always advocating for a future where technology serves the cause of freedom.